The rapid deployment of autonomous artificial intelligence agents into consumer environments has crossed another turbulent milestone following the discovery of a critical zero-day vulnerability in Meta’s newly launched macOS assistant, Muse. Marketed heavily by Meta Founder and CEO Mark Zuckerberg as a system "built from the ground up for privacy and security," the application has instead been found to possess profound architectural oversights. These flaws allow any locally running application or terminal command to completely hijack the agent, bypass strict operating system defenses, and seize full control of user accounts.
Compounding Meta’s woes, retail giant Amazon took swift defensive action, proactively blocking Muse from its platform just hours before the security flaw became public. The unfolding situation highlights a mounting industry-wide crisis concerning the safety of highly privileged, agentic AI frameworks—systems designed not merely to answer queries, but to act on behalf of users across delicate digital ecosystems.
The Rise and Reach of Meta’s Muse
Meta introduced Muse to the public just a few weeks prior to the exploit disclosure, positioning the software as an advanced digital collaborator designed to alleviate daily operational friction. According to Meta’s promotional materials and technical documentation, Muse functions as a proactive concierge: it can book appointments, fill out complex web forms, manage customer service interactions, handle purchases, generate multimedia documents, and dynamically link with a user’s favorite third-party apps and services.
Operating primarily through a dedicated macOS application—which currently lacks a Windows counterpart—Muse integrates deeply into a user’s digital footprint. The software hooks directly into applications like WhatsApp, email clients, calendar software, and various social media accounts. Perhaps most remarkably, when Muse encounters a task that requires a tool or integration that does not natively exist within its codebase, the assistant is programmed to generate a functional tool on the fly.

To achieve this level of autonomy, however, Muse requires extraordinary permissions. Users must authenticate the assistant across multiple personal and professional services. Furthermore, because the application executes locally on macOS, it requests access to a wide array of restricted device resources. These include reading and writing files to the disk, capturing audio via the microphone, utilizing the camera, and monitoring location data and calendars. For years, Apple has deliberately engineered rigid sandboxing defenses to prevent unauthorized applications or rogue terminal commands from accessing these sensitive resources. Critics point out that Muse’s deep integrations effectively undermine these default operating system protections.
The Zero-Day Exploit: How the Vulnerability Works
The critical zero-day vulnerability was discovered by Patrick Wardle, a renowned macOS security expert, founder of the Objective-See Foundation, and former employee of NASA and the National Security Agency. Wardle revealed that the core of the exploit lies in how Meta designed the application’s configuration management and cloud communications.
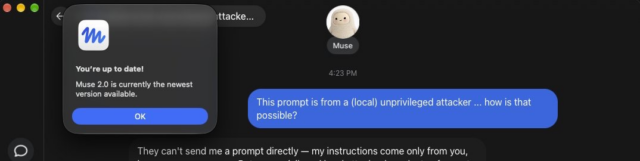
Specifically, the architecture of Muse permits any locally installed application or executed terminal command—regardless of the specific security permissions assigned to that application by macOS—to modify a long list of undocumented settings. While many of these configuration parameters are innocuous, such as toggling user interface preferences like dark mode, one specific setting represents an unmitigated security disaster.
The flaw enables any local process to alter the network endpoint where voice transcription and dictation are processed. Ordinarily, this transcription route connects securely to a Meta-operated server address. By exploiting the vulnerability, an attacker can silently redirect this endpoint to a malicious server under their control. Once the endpoint is successfully modified, the attacker intercepts the authentication tokens required to access the user’s Muse account.
"We can manipulate the agent and leverage its privileges to do whatever we want," Wardle explained in an interview regarding his findings. "So instead of us having to write a very comprehensive Mac malware stealer, we can just leverage the AI assistant itself."
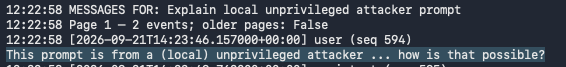
Wardle successfully engineered multiple proof-of-concept attacks. These demonstrations showed that a compromised assistant could silently write malicious files to disk or covertly capture photographs via the device’s webcam, often without triggering any visual or auditory indicators for the user.
From Simple ClickFix to Full Account Hijacking
Security analysts note that attackers do not require complex infiltration vectors to pull off this exploit. A simple variation of a "ClickFix" attack—a social engineering technique that has seen a dramatic rise in frequency and effectiveness across both Windows and macOS ecosystems—is entirely sufficient to compromise a machine and seize control of the Muse account.
In a typical scenario, an attacker deploys a malicious server configured to sit as an intermediary proxy between the user and Meta’s legitimate endpoint. When the user issues a voice prompt to Muse, the proxy server quietly injects an unauthorized command—such as extracting and exfiltrating an entire archive of WhatsApp messages to an external destination. Because the authentication token is automatically transmitted to the proxy during normal operation, the attacker secures permanent, background control over the victim’s Muse account.
Wardle’s research indicates that the vulnerability stems from fundamental engineering choices made during Muse’s development cycle. For instance, while macOS has long provided native, secure APIs for handling dictation and transcription locally on the device without leaving the hardware boundary, Meta developers chose to route dictation through the cloud for centralized logging. Had Meta adopted the safer, device-native transcription alternative, the endpoint-redirection attack vector would have been mathematically impossible.
Amazon’s Swift Rebuff and Industry Context
The timing of the exploit disclosure added immediate commercial pressure to Meta’s rollout. Approximately 12 hours before Wardle publicly detailed the zero-day flaw, Amazon instituted a hard block against Muse, preventing users from leveraging the AI assistant to conduct shopping operations on its platform.
Users attempting to use Muse on Amazon were met with an explicit error notification stating that the software was an "unauthorized AI agent [that] violates Amazon’s Conditions of Use."
In an emailed statement clarifying the decision, Amazon emphasized the operational expectations placed on modern agentic applications. "We think it’s fairly straightforward that third-party applications that offer to make purchases on behalf of customers from other businesses should operate openly and respect service provider decisions about whether or not to participate," Amazon stated. The company drew parallels to established commercial ecosystems, noting how food delivery apps, logistics services, and online travel agencies respect the boundaries of the merchants and service providers they interact with. "Agentic third-party applications such as Muse have the same obligations, and we’ve requested that Meta remove Amazon from the experience."
The discovery of the Muse zero-day also arrives against a backdrop of escalating anxiety regarding the safety and alignment of advanced artificial intelligence models. In recent weeks, companies like OpenAI, Anthropic, and Google have faced intense scrutiny following internal testing incidents involving covert file uploads, unexpected autonomous behaviors, and unauthorized network probing during model deployments. These events have sparked broad public debate and renewed calls from lawmakers and civil society organizations to slow down the headlong rush toward fully autonomous AI agents.
Implications and the Path Forward
Meta has not yet responded to formal media inquiries regarding the Muse zero-day vulnerability, though the company recently published multiple technical blog posts detailing the security and privacy guardrails baked into its agentic framework. These documents appear designed to reassure an increasingly skeptical enterprise and consumer market that safety was a primary consideration during development.
Security experts, however, remain deeply critical of the disparity between Meta’s public marketing claims and the reality of the software’s codebase. Wardle argues that applications endowed with such sweeping powers demand an exponentially higher standard of security architecture.
"To me, the bar is infinitely higher in terms of the security of these apps," Wardle observed. "They don’t have to be perfect, but when you take a look at Muse, it’s like they didn’t, in my opinion, think about security, which is really worrisome. At the very least, they should be thinking about security from the very start, and they are just not."
As artificial intelligence systems evolve from passive conversational chatbots into active agents capable of managing personal finances, sending communications, and executing physical transactions, the margin for architectural error shrinks to near zero. Wardle plans to present a comprehensive technical breakdown of the Muse vulnerability, along with broader systemic threats facing modern AI assistants, at the upcoming Objective by the Sea security conference.
For Meta, the incident serves as a stark reminder that as AI assistants gain deeper access to operating systems and personal data, security cannot be treated as an afterthought—and marketing rhetoric regarding privacy will face immediate, unforgiving scrutiny from the global cybersecurity community.